
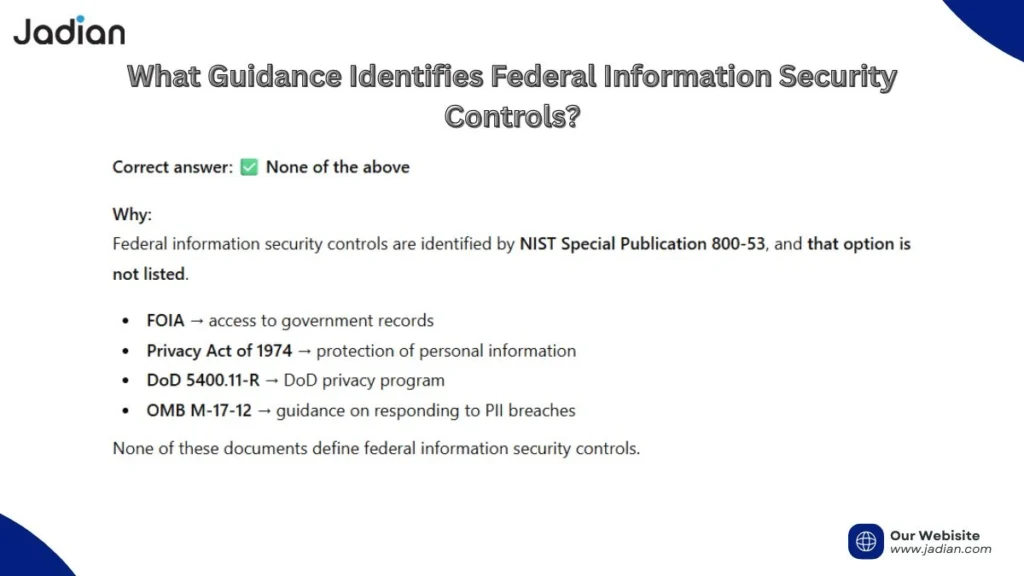
The most famous guide is the NIST Special Publication 800-53. It’s a massive catalog of security controls, like a giant IKEA manual for data protection. If you want to know how to authenticate a user (fancy-speak for “make sure it’s really you”), you’ll find the plan there.
Then there’s the Federal Information Security Modernization Act (FISMA). FISMA is the boss who says, “You must follow the recipe.” It’s the law that forces agencies to use NIST’s controls. No skipping steps, or you get a big, red audit flag.
Another key resource is the NIST Risk Management Framework (RMF). This is the step-by-step process for choosing and using those controls. It’s like the instructions that come with the IKEA furniture: “First, categorize your data. Second, select controls. Third, implement them. Fourth, don’t cry.”
Why This Matters for Your Morning Coffee
You might think, “I don’t work for the Pentagon, so who cares?” Well, you care when your tax return doesn’t end up in a hacker’s basement. Federal controls protect the systems that process your refund, your Medicare, and your student loans.
When your online banking app asks for a second code via text, that’s a control inspired by these same federal rules. It’s called multi-factor authentication, and it’s the same tech a spy might use to log into a secret database. You get the benefit without the secret handshake.
 Federal Information Security Controls: FISMA & NIST Guide
Remember the Office of Personnel Management (OPM) hack a few years back? That happened partly because some controls were weak. The guidance we’re talking about exists to prevent those massive breaches where your background check data goes for a stroll.
The Real-World Wardrobe Analogy
Think of federal security controls as a dress code for a very important party. NIST 800-53 is the list of acceptable outfits: “You may wear a tuxedo (encryption), a blazer (firewall), or a bow tie (password policy).”
FISMA is the host who checks at the door: “Sorry, no flip-flops (weak passwords) allowed.” And the RMF is how you pick your outfit: “Since I’m guarding the pentagon files, I’ll choose the full tuxedo. For my lunch coupon app, a polo shirt will do.”
The fun part? You can borrow this idea. When you set a really strong password or turn on two-factor authentication for your own email, you’re acting like a tiny federal agency. You’re choosing a control from your own mental catalog.
 What Guidance Identifies Federal Information Security Controls? - Jadian
A Little Story for Your Smile
A buddy of mine once managed a server that held cookie recipes for a kids’ camp. He used the same NIST controls as a top-secret lab. Why? Because those recipes had kids’ names and allergies. He laughed, but he slept better at night.
Another friend put a physical lock on her home router after reading a FISMA summary. She said, “If it’s good enough for the Department of Defense, it’s good enough for my Netflix.” She’s not wrong—controls are just common sense with a fancy government title.
So, next time you hear “federal information security controls,” don’t zone out. Think of it as the unsung hero of your digital life. It’s the reason your online doctor visit stays private, and why your credit card doesn’t party with your fridge.
These documents are the quiet guardians, making sure the government’s digital dance floor doesn’t get crowded with unwanted guests. And for that, we can all take a secure sip of our morning coffee.

